Introduction: AI Agents Need Their Own Identity
AI agents now run around the clock. They call APIs, read customer data, open pull requests and post to Slack, often with no human watching each step.
Yet most of them authenticate the same way: with a shared API key pasted into an environment variable. That key rarely expires, is rarely scoped, and leaves no record of which agent did what.
That gap is what agentic authentication and authorization closes. This guide explains what it is, why traditional identity tools fall short, and how to secure AI agents and MCP servers with the same rigor you apply to human users.
Why Traditional IAM Falls Short for AI Agents
Classic identity and access management tools such as Okta and Azure AD were designed for employees logging in. Their model assumes a person, a browser, a password or passkey, and a session that ends.
AI agents break every one of those assumptions:
                     HUMAN USERS                      AI AGENTS
When they act        Working hours, in sessions       24/7, continuously
How they sign in     Browser, password, passkey, MFA  API calls, often with a static key
What they touch      Apps they open                   Any tool or API their code can call
Who approves access  IT and managers                  Often no one
What gets logged Logins and admin changes Frequently nothing per actionThe result is a growing layer of non-human identity that sits outside governance. Shared API keys with no expiry become the default, and a single leaked key can expose every system an agent can reach.
Agentic auth does not replace your workforce identity provider. It extends the same principles, verified identity, least privilege and full audit, to the agents your teams are now deploying.
How to Secure MCP Servers
The Model Context Protocol (MCP) is how AI agents discover and call tools. Out of the box, an MCP server has no built-in access control, so any client that can reach it can call any tool it exposes.
MCP authentication and authorization fixes that by checking every request in real time:
1. Extract the token   from the incoming MCP request
2. Validate it         against the issuer's public keys (JWKS)
3. Check the scopes    against the tool being called
4. Log the decision    allowed or denied, to the audit trail
Two details make this practical at scale. Policy evaluation should be fast enough to run on every call; AuthSec reports under 5 ms per request. And MCP clients should configure themselves: by publishing standard discovery endpoints (authorization server metadata, OIDC configuration and JWKS), clients find every auth URL automatically, with no per-environment config files.
Delegation: When an AI Agent Acts on Behalf of a User
Many agents work for a specific person: a support bot answering a customer, or an assistant updating someone's CRM records. The agent should get that person's access, and nothing more.
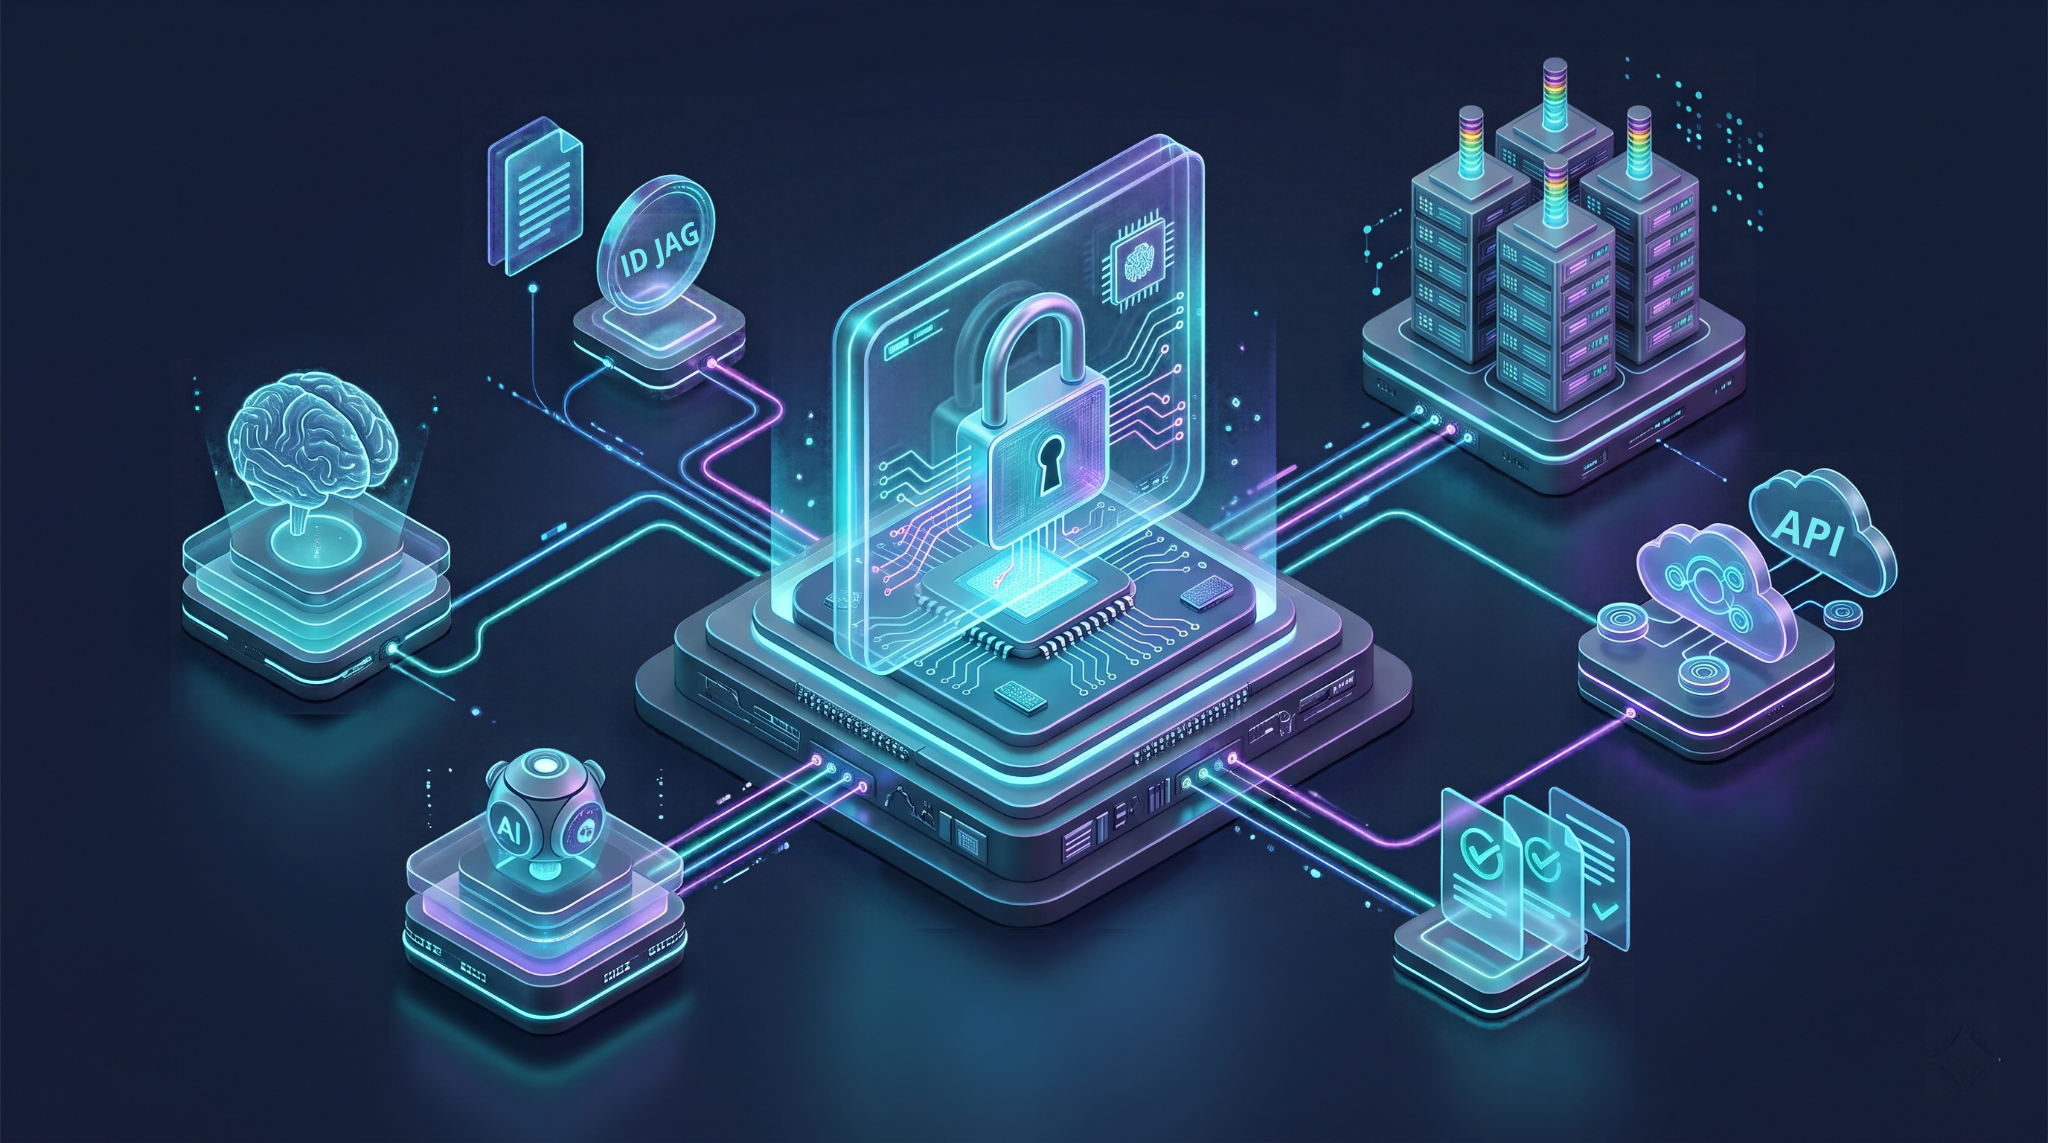
ID-JAG delegation handles this. The agent borrows the permissions of a signed-in user while keeping its own identity. For example, agent://support-bot acting for maya@acme.com can only reach what Maya can reach.
This gives you three guarantees that shared service accounts cannot:
- Bounded access. The agent never exceeds the delegating user's permissions.
- Dual attribution. Every action is traceable to both the agent and the user.
- Independent revocation. You can cut off the agent, the user, or both, at any time.
Machine-to-Machine Authentication
Agentic systems also include backend services, CI/CD jobs and devices that never open a browser. They need identity too. There are three ways a machine proves its identity:
- Client secret: a client ID and secret. Best for simple, trusted backend services.
- Private-key JWT: the service signs an assertion with its own private key, so no shared secret crosses the wire. Best for services that should never share secrets.
- SPIFFE SVID: a short-lived X.509 workload identity. Best for Kubernetes and service-to-service mTLS.
CIBA: Sign-In for Devices With No Browser
Client-Initiated Backchannel Authentication (CIBA) lets a voice assistant, IoT device or CLI tool request access while the user approves on their phone:
1. The device starts the request with the user's identifier
2. A push notification lands on the user's trusted phone
3. The user approves, or enters a TOTP code if push is unavailable
4. The device receives its tokens
No password is ever spoken to a speaker or typed into a terminal. Typical uses include Alexa, Google Assistant, smart devices and command-line tools.
Governance: One System for Humans and AI Agents
Authentication proves identity; governance keeps access correct over time. Agentic identity governance and administration (Agentic IGA) applies familiar controls to agents as well as employees.
The benefit of one platform is one audit trail. Security teams can answer "who accessed this data?" without stitching together logs from a workforce IdP, a secrets manager and a dozen agent frameworks.
- Access requests and approvals. When an agent tries to reach something it hasn't been granted, the request goes to "pending" until an admin approves it with a role.
- Role-based permissions. Agents and people share one RBAC model and one policy engine.
- Directory sync. Connect Active Directory, Entra ID or any SCIM 2.0 source so joiners get access automatically and leavers are deprovisioned automatically.
- Agent self-registration. A new agent registers itself with one API call and is classified as a human app, agent, M2M service or CLI, with no IT ticket.
How AuthSec Approaches Agentic Auth
AuthSec is an open-source identity and access management platform built to secure humans and AI agents under one system, with one policy engine and one audit trail.
It is built entirely on 13 open standards, including OAuth 2.1 with PKCE, OIDC, SAML 2.0, SCIM 2.0, FIDO2, SPIFFE, mTLS, CIBA, ID-JAG and MCP. The code is Apache 2.0 licensed on GitHub, and you can self-host on AWS, GCP, Azure or on-prem, or use the managed cloud.
It is organized into three products:
- Agent Security for AI agents and MCP servers: verified identity, tool-level access control and per-action logging.
- Agentic IGA for governance: approvals, roles, directory sync and audit, extended to agents.
- CIAM for human login: SSO, SAML, Okta, Azure AD, Google, passkeys (FIDO2/WebAuthn) and CIBA.
How It Compares
Most established auth platforms are strong at human login. Based on AuthSec's own comparison of publicly available information (October 2026), none of the alternatives below cover AI agent identity:
Capability                          AuthSec  Auth0 (Okta)  WorkOS       Stytch       Scalekit
AI agent identity                   Yes      No            No           No           No
MCP server protection               Yes      No            No           No           No
Humans and agents in one platform   Yes      No            No           No           No
Workload identity (SPIFFE / X.509)  Yes      No            No           No           No
Audit log covering agents           Yes      Humans only   Humans only  Humans only  Humans only
Open source / self-hostable         Yes      No            No           No           No
Enterprise SSO and SCIM Yes Yes Yes Yes YesAuthSec doesn't have to replace your workforce IdP. Many enterprises keep Okta for employees and add AuthSec for the agent layer.
Getting Started: Protect an MCP Server in One Call
Agentic auth only works if developers actually adopt it. AuthSec ships official SDKs for Python, TypeScript and Go, and one function mounts authentication on any MCP server path.
pip install authsec-sdk          # Python
npm install @authsec/sdk         # TypeScript
go get github.com/authsec-ai/sdk-authsec/packages/go-sdk # Gofrom authsec_sdk import mount_mcp, Config
cfg = Config.from_env() # reads AUTHSEC_* env vars
mount_mcp(app, "/mcp", handler, cfg)
# Every call to /mcp now requires a valid token and the right scopesFrom there, every request is validated, scope-checked and logged. AuthSec says teams can go from install to a first enforced policy in production in a single afternoon. Full guides are at docs.authsec.dev.
Conclusion: Give Every AI Agent an Identity
AI agents are becoming some of the most active identities in your organization. Securing them with shared API keys is the equivalent of giving every employee the same password.
Agentic authentication and authorization fixes that with a verified identity per agent, credentials that expire in minutes, least-privilege scopes on every call, safe delegation, and an audit trail that covers humans and agents alike.
Ready to secure your agents and MCP servers? Start free at authsec.ai with no credit card, book a 30-minute demo at authsec.ai/contact, or explore the quickstarts at docs.authsec.dev.